Key Takeaways
- Penetration testing best practices require a structured, phased approach. Ad hoc testing misses the attack paths that determined adversaries actually use.
- Running pen tests once or twice a year is not enough. Major infrastructure changes, new releases, and security incidents each warrant an immediate test.
- Thinking like an attacker is the mindset shift that separates effective pen testing from checkbox compliance.
- Scope definition before testing and retesting after every remediation are the two steps most teams skip. Both are non-negotiable in any serious pen testing program.
- The right tool lets you track findings, manage remediation, and demonstrate coverage progress to stakeholders across every phase.
Here are seven tips that put these principles into practice. 👇
All developers and testers understand that much planning goes into an attack, whether a minor attack or an attempt to compromise data. This prompts developers to put forth a lot of effort to prevent someone like “Angelina” from hacking their product in less than three minutes.
In many ways, testing the readiness of your product to withstand attacks is the responsibility of the engineers. Therefore, the better their strategy for penetration tests, the higher their chances of finding all possible vulnerabilities within the system.
The Core Phases of a Penetration Testing Workflow
Following pen testing best practices starts with understanding the structure of the process itself. Each phase builds on the one before it. Skipping a phase does not save time; it produces gaps that attackers find before your next test does.
Phase 1: Planning and reconnaissance.
Define objectives, scope, and rules of engagement before anything else. Gather publicly available information about targets: IP ranges, domain names, employee data, and technology stack details. The quality of this phase determines the quality of everything that follows.
Phase 2: Scanning and enumeration.
Use automated and manual tools to identify open ports, running services, and potential entry points. Enumerate user accounts, shared resources, and application endpoints. The goal is building a complete picture of the attack surface before any exploitation attempt begins.
Phase 3: Exploitation.
Attempt to exploit identified vulnerabilities and gain access. This is where penetration testing best practices diverge most sharply from vulnerability scanning: exploitation confirms whether a weakness is real and measurable, not theoretical. Document every successful and failed attempt with evidence.
Phase 4: Post-exploitation and lateral movement.
Once access is gained, test how far an attacker could move. Can they escalate privileges? Reach sensitive data? Access other systems? This phase reveals the actual blast radius of a successful attack, not just the entry point.
Phase 5: Reporting.
Compile findings into a report covering what was tested, what was found, how it was exploited, and recommended remediation steps. Prioritise by severity. Include evidence: screenshots, logs, and reproduction steps that developers can act on without ambiguity.
aqua cloud supports the full pentest lifecycle. Teams use it to manage test cases across all five phases, log findings with visual evidence through Capture, and track remediation from discovery to closure in one platform.
Keep falling into a rabbit hole
Wikipedia is considered the most popular source for falling into a rabbit hole. It would be a crime not to use this principle to avoid mistakes during your penetration testing — “…according to the principle of obliquity, the meandering path may eventually be more productive than a direct approach.”
Vulnerabilities are likely connected, creating a path of attack.
You must find at least one vulnerability and explore every device, browser, database, etc. This will identify possible loopholes, weaknesses and prevention methods for each discovered issue.
Stop treating Pen tests like a dentist appointment
Pentesting isn’t like your dentist appointment. Yeah, yearly check-ups are recommended, but when you finally show up, there’s already a massive cavity in your tooth. So that’s why it is better to have regular check-ups even if it seems unnecessary.
HelpSystems research shows most respondents only run pen testing once or twice a year (16% twice a year, 17% quarterly); that’s not good.
Unfortunately, a lack of regular testing can give hackers more time to plan different attack methods.
Assess business objectives VS risks
If you still think that a business consists of a group of dudes sitting in a conference room talking about money, devoid of QA, you’re being shortsighted. Business always correlates with risk, and so do the measures undertaken to mitigate these risks; this defines exemplary businesspeople.
So take a look into your company’s security goals to set a better pentest workflow: what are they based on, what assets are critical and what can be addressed later? As soon as you assess all risks, you can undertake appropriate remediation efforts towards mitigating malware attacks and establishing the strongest penetration testing workflow.
Stop relying on trust for luck
Many QA newbies rely on serendipitous discoveries while testing. They tend to stick to this ideology regarding their system’s protection. They hope developers didn’t leave an opening for hacker intervention; that’s foolish because hackers don’t think this way.
aqua cloud's AI Copilot generates structured pen test cases from requirements in seconds
Define the Scope Before Anything Starts
Penetration testing without a defined scope produces inconsistent results and legal exposure. Your team wastes time on areas that do not matter while missing the ones that carry real risk.
Define exactly what is in scope: specific IP ranges, applications, environments, and user roles. Document what is out of scope just as clearly. Get a signed scope agreement in place before a single test runs.
Scope creep during a pentest is one of the most common causes of incomplete findings. When testers follow a thread beyond agreed boundaries, results become unverifiable and comparisons between test cycles break down. A clear scope document solves this before it starts.
Retest Every Vulnerability After Remediation
Fixing a reported vulnerability is not the same as closing it. Development teams often patch the specific issue described in the report while the underlying condition that allowed it remains. Retesting confirms the fix actually works.
After each remediation cycle, run targeted tests against every issue that was reported. Do not wait for the next full engagement. Partial fixes are common, and retesting catches them before they reach production.
Track retest results against the original findings in your test management tool. This creates a clear record of what was fixed, when, and by whom. aqua cloud links retest results directly to original defect reports, so your audit trail is complete without extra documentation effort.
To ensure they have the correct target, they must identify and research every available device, application or database.
The best QA engineers usually walk a similar path — they think like a criminal; to beat them at their own game. So take a minute, and consider what you would do if you wanted to cause a breach or compromise specific data. Please create and document test cases for each of these steps.
95% of users noted improvements in their QA after a month with aqua
Choose your fighter wisely
Let’s say you’ve already done everything we described above… but want to go even further. Using the proper agile testing tool is an excellent opportunity to enhance penetration testing.
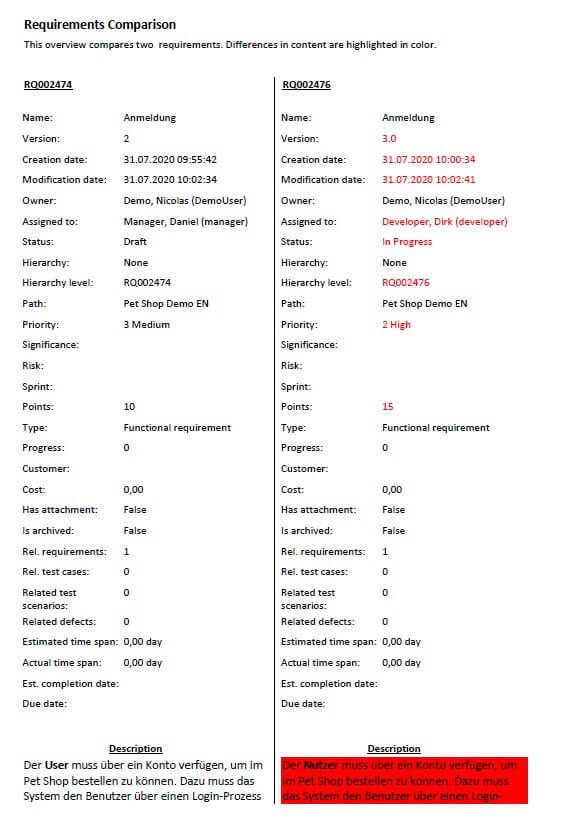
As it’s a common practice to make changes in your product infrastructure after penetration testing, it would be awesome to see the difference before and after. For example, aqua has a function for super detailed reporting which can depict, in percentage, how much each part of the system remains untested or unprotected. To summarise, try to find a comprehensive test management solution.
Conclusion
Penetration testing remains a pillar of high-quality products. You can’t underestimate its impact even though there’s still a big chance to screw it up, no matter how fantastic your penetration testing platform or your test cases game is. Only a complex and pervasive approach, with a strong plan, can achieve satisfactory results for your pen testing. However, in a bundle with the tips we’ve given you in this article, you can significantly enhance this approach.
Discover aqua for better penetration testing