We use cookies and third-party services that store or retrieve information on the end device of our visitors. This data is processed and used to optimize our website and continuously improve it. We require your consent fro the storage, retrieval, and processing of this data. You can revoke your consent at any time by clicking on a link in the bottom section of our website. Privacy Policy.
Customise Consent Preferences
We use cookies to help you navigate efficiently and perform certain functions. You will find detailed information about all cookies under each consent category below.
The cookies that are categorised as "Necessary" are stored on your browser as they are essential for enabling the basic functionalities of the site. ...
Always Active
Necessary cookies are required to enable the basic features of this site, such as providing secure log-in or adjusting your consent preferences. These cookies do not store any personally identifiable data.
Cookie
gf_email_otp_seed_3
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
gf_email_otp_seed_12
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
gf_email_otp_seed_6
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
gf_email_otp_seed_1
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
gf_email_otp_seed_4
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
gf_email_otp_seed_10
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
gf_email_otp_seed_5
Duration
2 hours
Description
Used to temporarily store the OTP verification seed required for secure form or email verification.
Cookie
VISITOR_PRIVACY_METADATA
Duration
6 months
Description
YouTube sets this cookie to store the user's cookie consent state for the current domain.
Cookie
GAESA
Duration
1 month
Description
Description is currently not available.
Cookie
aquaSessionId2
Duration
2 days
Description
Description is currently not available.
Cookie
aquaXAuthId2
Duration
2 days
Description
Description is currently not available.
Cookie
rc::a
Duration
Never Expires
Description
This cookie is set by the Google recaptcha service to identify bots to protect the website against malicious spam attacks.
Cookie
rc::c
Duration
session
Description
This cookie is set by the Google recaptcha service to identify bots to protect the website against malicious spam attacks.
Cookie
__Secure-ENID
Duration
1 year 1 month
Description
The __Secure-ENID cookie is a type of secure cookie used for authentication and to ensure the security of user sessions.
Cookie
LS_CSRF_TOKEN
Duration
session
Description
Cloudflare sets this cookie to track users’ activities across multiple websites. It expires once the browser is closed.
Cookie
zalb_*
Duration
session
Description
Zoho sets this cookie for load balancing and session stickiness. It ensures that user requests are consistently directed to the same server during a session, helping maintain session integrity and improving website performance.
Cookie
GCLB
Duration
session
Description
This cookie is known as Google Cloud Load Balancer set by the provider Google. This cookie is used for external HTTPS load balancing of the cloud infrastructure with Google.
Cookie
cookieyes-*
Duration
1 year
Description
CookieYes sets this cookie for consent solution management.
Cookie
__cf_bm
Duration
1 hour
Description
This cookie, set by Cloudflare, is used to support Cloudflare Bot Management.
Functional cookies help perform certain functionalities like sharing the content of the website on social media platforms, collecting feedback, and other third-party features.
Cookie
VISITOR_INFO1_LIVE
Duration
6 months
Description
A cookie set by YouTube to measure bandwidth that determines whether the user gets the new or old player interface.
Cookie
ytidb::LAST_RESULT_ENTRY_KEY
Duration
Never Expires
Description
The cookie ytidb::LAST_RESULT_ENTRY_KEY is used by YouTube to store the last search result entry that was clicked by the user. This information is used to improve the user experience by providing more relevant search results in the future.
Cookie
__session
Duration
1 year 1 month 4 days
Description
GitBook sets this cookie for logging in.
Cookie
uesign
Duration
1 month
Description
Zoho sets this cookie for the Visitor Live Chat.
Cookie
_tldtest_*
Duration
session
Description
Amplitude sets this cookie to determine the highest-level domain where cookies can be set. Deleted after testing.
Cookie
lidc
Duration
1 day
Description
LinkedIn sets the lidc cookie to facilitate data center selection.
Cookie
li_gc
Duration
6 months
Description
Linkedin set this cookie for storing visitor's consent regarding using cookies for non-essential purposes.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics such as the number of visitors, bounce rate, traffic source, etc.
Cookie
gf_visitor_source
Duration
7 days
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
gf_visitor_medium
Duration
7 days
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
gf_visitor_campaign
Duration
7 days
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
gf_visitor_content
Duration
7 days
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
gf_visitor_term
Duration
7 days
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
gf_visitor_location
Duration
7 days
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
ga_session_duration
Duration
1 hour
Description
Stores visitor attribution data such as source, medium, campaign, content, term, and location for analytics and lead attribution.
Cookie
_ga_*
Duration
1 year 1 month 4 days
Description
Google Analytics sets this cookie to store and count page views.
Cookie
_ga
Duration
1 year 1 month 4 days
Description
Google Analytics sets this cookie to calculate visitor, session and campaign data and track site usage for the site's analytics report. The cookie stores information anonymously and assigns a randomly generated number to recognise unique visitors.
Cookie
amp_*
Duration
1 year
Description
Amplitude sets this cookie for session tracking for analytics purposes.
Cookie
YSC
Duration
session
Description
YSC cookie is set by Youtube and is used to track the views of embedded videos on Youtube pages.
Cookie
amplitude_device_id
Duration
session
Description
No description available.
Cookie
loom_anon_comment
Duration
1 year
Description
No description available.
Cookie
loom_referral_video
Duration
session
Description
Description is currently not available.
Cookie
__Host-psifi.analyticsTrace
Duration
6 hours
Description
Description is currently not available.
Cookie
__Host-psifi.analyticsTraceV2
Duration
6 hours
Description
Description is currently not available.
Cookie
_cs_id
Duration
1 year 1 month
Description
This cookie is used to store the ContentSquare's user identifier ID. This is a persistent cookie and expires after 13 months.
Cookie
_cs_s
Duration
1 hour
Description
This cookie is used to store the number of page's viewed by a visitor within the session for ContentSquare's solution.
Cookie
ai_session
Duration
1 hour
Description
This is a unique anonymous session identifier cookie set by Microsoft Application Insights software to gather statistical usage and telemetry data for apps built on the Azure cloud platform.
Cookie
_hjSessionUser_*
Duration
1 year
Description
Hotjar sets this cookie to ensure data from subsequent visits to the same site is attributed to the same user ID, which persists in the Hotjar User ID, which is unique to that site.
Cookie
_hjSession_*
Duration
1 hour
Description
Hotjar sets this cookie to ensure data from subsequent visits to the same site is attributed to the same user ID, which persists in the Hotjar User ID, which is unique to that site.
Cookie
ajs_anonymous_id
Duration
1 year
Description
This cookie is set by Segment to count the number of people who visit a certain site by tracking if they have visited before.
Cookie
_cs_c
Duration
1 year 1 month
Description
This cookie is used by Contentsquare to store the user's consent preference for analytics and session replay tracking.
Cookie
utm_medium
Duration
7 days
Description
This cookie is used to record from where the visitor came to the website orginally. This information is used by the website operator to know the efficiency of their marketing.
Cookie
utm_source
Duration
7 days
Description
This cookie is used to record from where the visitor came to the website orginally. This information is used by the website operator to know the efficiency of their marketing.
Cookie
utm_campaign
Duration
7 days
Description
Google Ad Services sets this cookie to store session campaign value if present.
Cookie
utm_content
Duration
7 days
Description
This cookie is used for storing the session content value if present.
Cookie
utm_term
Duration
7 days
Description
This cookie is used to record from where the visitor came to the website orginally. This information is used by the website operator to know the efficiency of their marketing.
Cookie
amp_cookie_test*
Duration
session
Description
Amplitude sets this cookie to test if cookies are enabled in the user’s browser. It is used during SDK initialisation and is automatically removed after the check.
Cookie
utsdb
Duration
session
Description
Zoho SalesIQ sets this cookie to register data on visitor's website behaviour.
Performance cookies are used to understand and analyse the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Cookie
_uetsid
Duration
1 day
Description
Bing Ads sets this cookie to engage with a user that has previously visited the website.
Cookie
_uetvid
Duration
1 year 24 days
Description
Bing Ads sets this cookie to engage with a user that has previously visited the website.
Advertisement cookies are used to provide visitors with customised advertisements based on the pages you visited previously and to analyse the effectiveness of the ad campaigns.
Cookie
_gcl_au
Duration
3 months
Description
Google Tag Manager sets this cookie to experiment advertisement efficiency of websites using their services.
Cookie
__Secure-ROLLOUT_TOKEN
Duration
6 months
Description
YouTube sets this cookie to manage feature rollout and experimentation. It helps Google control which new features or interface changes are shown to users as part of testing and staged rollouts, ensuring consistent experience for a given user during an experiment.
Cookie
__Secure-YEC
Duration
past
Description
Description is currently not available.
Cookie
__Secure-YNID
Duration
6 months
Description
YouTube cookie used to protect user security and prevent fraud, especially during the login process.
Cookie
test_cookie
Duration
15 minutes
Description
doubleclick.net sets this cookie to determine if the user's browser supports cookies.
Cookie
MUID
Duration
1 year 24 days
Description
Bing sets this cookie to recognise unique web browsers visiting Microsoft sites. This cookie is used for advertising, site analytics, and other operations.
Cookie
ai_user
Duration
1 year
Description
Microsoft Azure sets this cookie as a unique user identifier cookie, enabling counting of the number of users accessing the application over time.
Cookie
NID
Duration
6 months
Description
Google sets the cookie for advertising purposes; to limit the number of times the user sees an ad, to unwanted mute ads, and to measure the effectiveness of ads.
Cookie
__Host-GAPS
Duration
2 years
Description
This cookie allows the website to identify a user and provide enhanced functionality and personalisation.
Cookie
bcookie
Duration
1 year
Description
LinkedIn sets this cookie from LinkedIn share buttons and ad tags to recognize browser IDs.
Cookie
IDE
Duration
1 year 24 days 1 minute
Description
Google DoubleClick IDE cookies store information about how the user uses the website to present them with relevant ads according to the user profile.
Cookie
guest_id_marketing
Duration
1 year 1 month 4 days
Description
Twitter sets this cookie to identify and track the website visitor.
Cookie
guest_id_ads
Duration
1 year 1 month 4 days
Description
Twitter sets this cookie to identify and track the website visitor.
Cookie
personalization_id
Duration
1 year 1 month 4 days
Description
Twitter sets this cookie to integrate and share features for social media and also store information about how the user uses the website, for tracking and targeting.
Cookie
guest_id
Duration
1 year 1 month 4 days
Description
Twitter sets this cookie to identify and track the website visitor. It registers if a user is signed in to the Twitter platform and collects information about ad preferences.
Other uncategorised cookies are those that are being analysed and have not been classified into a category as yet.
Cookie
_cs_root-domain
Duration
session
Description
Description is currently not available.
Cookie
aquacloudio-_zldp
Duration
1 year 1 month 4 days
Description
Description is currently not available.
Cookie
aquacloudio-_zldt
Duration
1 year 1 month 4 days
Description
Description is currently not available.
Cookie
amplitude_testaqua-cloud.io
Duration
1 year
Description
Description is currently not available.
X
🤖 Exciting new updates to aqua Intelligence are now available! 🎉
Test and Requirement Management Compliance for European Business
Has your legal department already raised the compliance issue? For European businesses, it’s becoming increasingly difficult to find a test management software that would allow them to stay legal. Regulators demand proof of what you built, why you built it, and how you verified it works. This shift makes [test management systems](https://aqua-cloud.io/test-management-system-qa-process/) more of compliance-enabling platforms than yet another tool in your tech stack. This article will guide you through essential regulatory legislations for QA and show the role of a compliant QA platform for your business.
Regulatory frameworks like GDPR, NIS2, DORA, and MDR/IVDR all share a common expectation that organizations can demonstrate accountability through documented evidence.
Effective compliance requires structured test management with traceability from requirements to test execution, defects, fixes, and release documentation.
Requirements must be uniquely identified, versioned, traceable, and controlled with documented approval states to prove what was agreed upon.
Technology solutions like aqua, an AI-driven work OS, enforce compliance processes through automation, audit trails, and immutable logs rather than relying on manual processes.
European businesses face regulatory pressure that transforms QA from a quality tool into a compliance necessity. Want to know how to build a defensible framework that holds up under audit without drowning in bureaucracy? Read on 👇
Understanding Regulatory Compliance in Europe
Regulatory compliance in Europe is the system that ensures organizations adhere to relevant laws, regulations, and industry standards that govern operations. For your business, compliance in QA is basically demonstrating accountability through documented evidence.
European compliance operates on two levels. Cross-industry regulations like GDPR and NIS2 set baseline expectations, while sector-specific rules such as DORA for finance or MDR/IVDR for medical devices add additional layers. What unites these frameworks is the expectation that you can prove compliance through documented evidence chains.
Here are the key regulatory frameworks:
GDPR – Accountability and records of processing under Article 5(2), especially where test artifacts contain personal data. Your QA needs controlled access and audit logs for data protection governance
NIS2 – Cybersecurity risk-management measures, including supply chain security and secure SDLC practices. Your test and requirement processes demonstrate cyber hygiene through vulnerability handling and documentation integrity
DORA – ICT third-party risk management and operational resilience expectations for financial services. This includes oversight of critical ICT providers, which means your QA platform vendor falls under scrutiny
MDR/IVDR – Technical documentation and traceability requirements for medical devices and health software. You must demonstrate conformity assessment through complete verification records
Cloud Sovereignty Framework – Procurement expectations for SaaS platforms emphasizing strategic and operational autonomy for European organizations
Non-compliance risks extend beyond fines. You face reputation damage, operational disruption, and, in regulated sectors, blocked product releases. The question has evolved from “do we need a test tool?” to “can our test tool help us prove compliance?”
As stricter regulatory frameworks are enforced across Europe, the difficulty of maintaining defensible, audit-ready evidence continues to increase. aqua cloud, an AI-powered work OS, stands out specifically for European businesses by offering end-to-end traceability from requirements to test execution. This includes immutable audit logs that satisfy GDPR, NIS2, and sector-specific regulations like DORA. With its ISO 27001 certification and EU data center hosting options, aqua provides the security governance and sovereignty alignment that European regulators increasingly demand. The platform’s domain-trained Copilot automatically generates comprehensive test cases from requirements, documentation, and even voice notes, helping to save manual work on maintaining that critical evidence chain. Plus, aqua integrates with Jira, Azure DevOps, and 12+ of your existing development tools.
Save 80% of time on ensuring regulatory compliance with aqua’s capabilities
Test management in a compliance context focuses on running the right tests, documenting them properly, and proving your verification process is repeatable and traceable. Regulators and auditors care less about your team’s capability. Instead, they focus more on whether you can show that critical requirements were validated through documented tests with consistent results.
Structured test management processes create a defensible verification layer. Good test management means defining what “tested” actually means for your organization. You need to build an unbroken evidence chain from requirement through test design, execution, defect management, remediation, retesting, and final release.
Requirements traceability – Test cases link directly to requirements, particularly for high-risk and regulated features. Critical requirements have documented verification evidence available for auditor review.
Execution evidence capture – Timestamped test results include screenshots or logs for critical scenarios. This documentation provides audit-ready evidence beyond simple pass/fail flags.
Role-based access control – Separation of duties prevents testers from approving their own work. Clear approval workflows and authorization levels eliminate conflicts of interest.
Audit trail maintenance – Complete records show who executed which tests, when they ran, and what results emerged. Changes throughout the testing lifecycle are fully documented for accountability.
Regression validation – Affected functionality receives documented re-validation after changes. Regression strategies tie directly to specific change scope.
Coverage analysis – Test coverage meets defined thresholds through demonstrable metrics. Risk-based prioritization ensures regulatory requirements receive appropriate validation depth.
Evidence retention – Test artifacts, results, and supporting documentation remain accessible according to regulatory retention requirements and audit readiness standards.
Generally speaking, compliance testing isn’t too different from any other testing, you’re just getting the requirements from a 3rd party, and your PM might need to talk to legal to interpret some of the requirements.
Vague requirements live in scattered documents without an approved state and unclear ownership. Add the absence of a sign-off trail, and you can’t even prove what was agreed or when. Regulators expect requirements to be uniquely identified, versioned, traceable, and controlled. Changes need a documented impact assessment.
Clear and traceable requirements force early alignment between all parties. Business stakeholders, product teams, and compliance owners must agree on what “done” means. They also create a baseline for change control. When features change, you can trace which tests are affected, which risks might shift, and whether changes require re-approval.
Requirements Management Maturity Levels
Organizations typically progress through distinct maturity levels in their requirements management practices. Understanding these levels helps you identify gaps and prioritize improvements:
Maturity Level
Characteristics
Compliance Risk
Typical Tools
Ad-hoc
Requirements in emails, documents, informal discussions; no versioning or approval workflow
Critical – No audit trail, uncontrolled changes
Email, shared documents
Documented
Requirements captured in structured format; basic versioning but limited traceability
High – Incomplete evidence chain, manual tracking
Spreadsheets, wikis
Managed
Requirements with unique IDs, approval workflows, and traceability to tests; change control processes
End-to-end workflow automation, predictive risk analysis, unified work OS
Minimal – Proactive compliance monitoring
Work OS platforms
ISO/IEC/IEEE 29148 provides a solid reference for disciplined requirement specification. The standard defines attributes like unique ID, rationale, priority, acceptance criteria, and status. Adopting consistent requirement management principles with fields for risk tags builds compliance governance at the source. Add security considerations and data protection notes where relevant.
Key Challenges in Test and Requirement Management Compliance
You might encounter predictable roadblocks when operationalizing compliance through QA processes. These challenges in test management turn “we’ve got this” into scrambling during audit preparation.
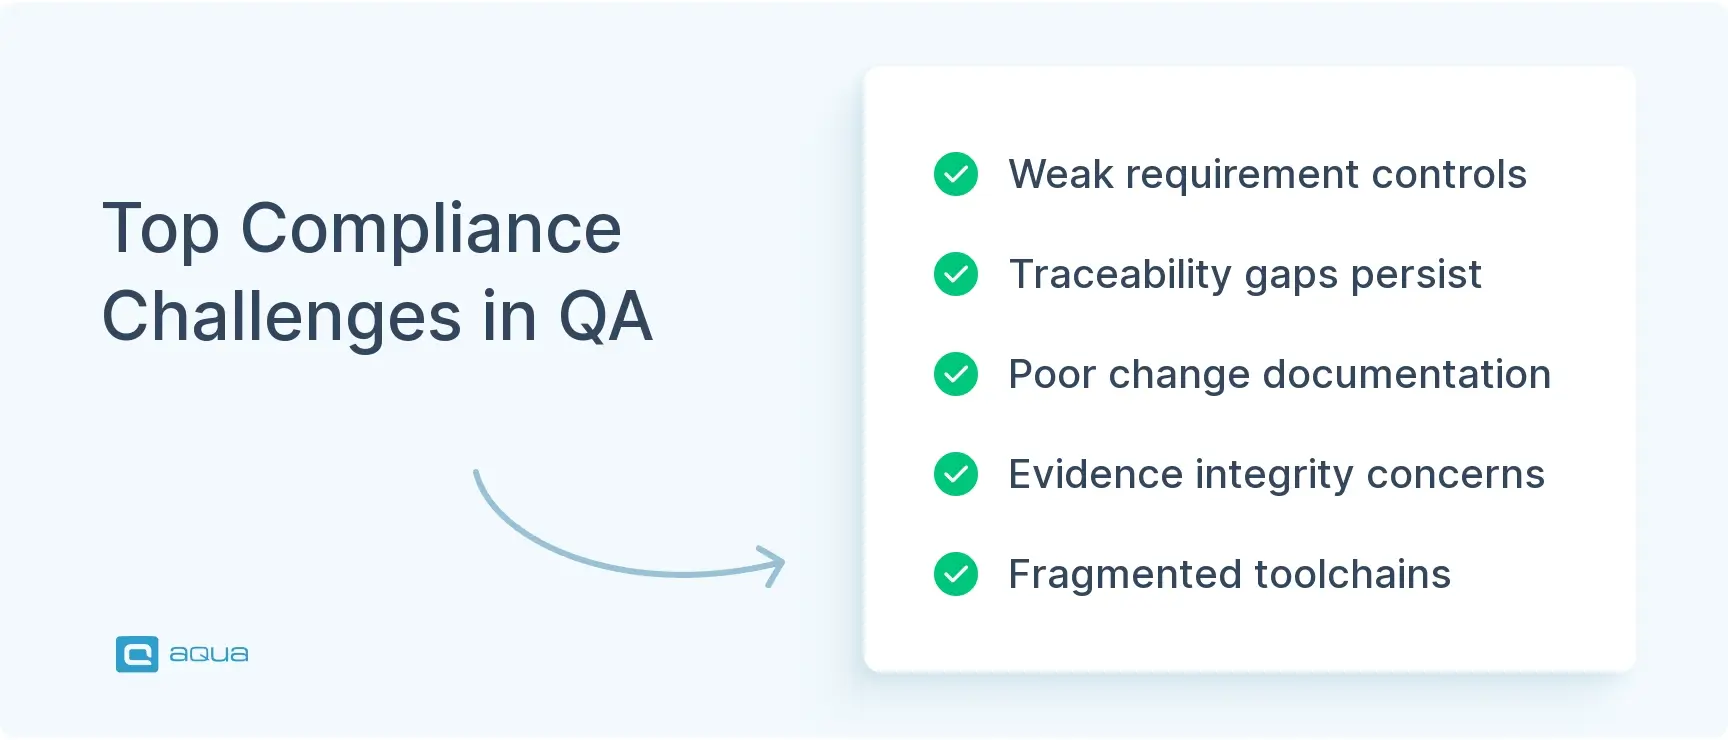
1. Weak Requirement Lifecycle Management
Requirements spread across documents, emails, or unstructured wikis lack approval states and change control. When features evolve during development, there’s no record of what changed or why. This makes it impossible to prove what you agreed to build. The “requirements drift” means your testers validate something different from what stakeholders approved, which breaks the link to test evidence.
Critical parameters affected:
Approval state tracking and sign-off trails for requirements baseline
Change history with rationale and impact assessment documentation
Version control linking requirements, iterations to specific releases
Ownership assignment with clear accountability for requirement validity
2. Traceability Gaps
Partial traceability, where some projects maintain links and others don’t, creates inconsistent evidence chains. Manual traceability matrices become stale within weeks because nobody updates them consistently. During audits, claiming “we tested the requirement” isn’t defensible. You must show which test validated it and what the result was.
Critical parameters affected:
Bidirectional trace links between requirements, tests, defects, and releases
Coverage metrics demonstrating complete validation of critical requirements
Impact analysis capabilities showing downstream effects of requirement changes
Gap identification revealing untested requirements or unlinked test cases
3. Poor Change Control
Changes get merged without updating requirements, while impact assessments are skipped or done informally. Regression testing isn’t traceable to change scope, which makes your release evidence contestable. You can’t prove the change didn’t introduce new risks without documenting which tests re-validated affected functionality.
Critical parameters affected:
Change request documentation with formal approval workflows and sign-offs
Impact assessment scope identifying affected requirements, tests, and components
Regression test selection tied to specific changes and risk profiles
Retest confirmation with evidence that the affected functionality was re-validated
4. Evidence Integrity Issues
Missing audit logs and unclear retention policies make test results unreliable for compliance purposes. Your test artifacts and attachments become questionable, leading auditors to distrust evidence integrity and question entire test campaigns.
5. Toolchain Fragmentation
Requirements in one system, tests in another, defects in a third create integration challenges where context gets lost. Identifiers don’t align across platforms. This forces teams to maintain the evidence chain through manual reconciliation, prone to errors.
Strategies for Effective Compliance Management
European compliance requires strategic approaches that align with regulatory expectations while maintaining operational efficiency. Here are proven strategies for building defensible compliance frameworks.
1. Risk-Based Compliance Prioritization
Focus your compliance efforts on high-risk requirements and critical functionality that regulators care about most. Not every requirement needs the same level of documentation rigor. By identifying and classifying requirements based on regulatory impact, your team can allocate resources where they matter most. Safety implications and data sensitivity guide prioritization decisions.
Implementation approach:
Classify requirements by regulatory impact using risk matrices that account for safety, security, data protection, and operational factors.
Apply tiered traceability where critical requirements receive mandatory bidirectional linking while lower-risk items use lighter documentation.
Prioritize test coverage for regulated features with deeper validation scenarios and more comprehensive evidence capture.
Review risk classifications periodically to adjust as regulations evolve or your product scope changes.
This strategy ensures your compliance investments target actual regulatory exposure while avoiding unnecessary overhead on low-risk functionality.
2. Automated Evidence Chain Management
Manual evidence gathering fails under pressure and creates gaps that surface during audits. Automation embeds compliance into your workflow by capturing evidence as work happens rather than reconstructing it later. When test execution automatically generates timestamped results, captures screenshots, and maintains audit trails, compliance becomes a byproduct of normal operations.
Implementation approach:
Integrate test execution into CI/CD pipelines so every deployment has associated test evidence tied to specific code changes.
Configure automated traceability updates that maintain requirement-to-test links as changes occur across your toolchain.
Enable immutable audit logging for critical actions like requirement approvals, test result modifications, and release sign-offs.
Set up retention policies that preserve evidence according to regulatory requirements without manual archiving efforts.
This strategy transforms compliance from a separate activity into an automated aspect of your development process.
3. Unified Compliance Platform Strategy
Toolchain fragmentation breaks evidence chains and creates reconciliation overhead. A unified platform approach minimizes integration points where context gets lost. When requirements, tests, and execution results live in a single system, evidence integrity improves dramatically. This happens through consistent identifiers and built-in traceability that removes manual synchronization.
Implementation approach:
Consolidate test and requirement management onto platforms with native traceability rather than relying on fragile integrations.
Establish a single source of truth for requirement definitions with version control and approval workflows in one location.
Implement role-based access control across the entire compliance evidence chain to enforce separation of duties.
Create standardized export templates that package requirements, tests, and results for audit requests.
This strategy reduces the number of systems that must align for compliance while simplifying evidence retrieval during audits.
4. Continuous Compliance Validation
Waiting until audit preparation to check compliance readiness creates crisis situations when gaps appear. Continuous validation means regularly verifying that your evidence chains are complete. Your traceability stays current and your controls work as intended. Internal audits and spot checks catch problems early when they’re easy to fix.
Implementation approach:
Schedule monthly traceability audits that sample requirements and verify complete links to test evidence and execution results.
Run automated compliance reports checking for untested requirements, missing approval states, and evidence gaps.
Conduct quarterly mock audits where your team practices responding to typical auditor requests within defined timeframes.
Track compliance metrics over time to identify patterns like specific teams or projects with recurring gaps.
This strategy shifts compliance from reactive fire-fighting to proactive risk management where early warning systems give you time to remediate issues.
5. Stakeholder Alignment and Training
Compliance fails when people don’t understand why it matters or how to do it properly. Your team members need clarity on what regulators expect and what their individual responsibilities are. Training builds competency while alignment ensures everyone works toward the same compliance objectives.
Implementation approach:
Develop role-specific training on compliance requirements, tooling capabilities, and documentation standards for different team members.
Create compliance champions within your teams who understand regulations deeply and can guide peers through complex scenarios.
Document compliance procedures with practical examples showing correct requirement writing, test linking, and evidence capture.
This strategy ensures compliance knowledge spreads throughout your organization rather than concentrating expertise in just a few people.
Compliance testing usually refers to testing regulatory requirements (such as hardware/software passing certain ISO criteria). It’s usually a set of external requirements.
Using aqua cloud Test and Requirement Management Capabilities
aqua cloud provides a test and requirement management solution specifically designed to address European compliance challenges. As an integrated platform, aqua cloud eliminates the toolchain fragmentation that typically breaks evidence chains. The system offers end-to-end traceability from requirements through test execution to release documentation within a single environment.
The platform’s compliance foundation starts with deployment flexibility featuring EU data center hosting options. These satisfy data residency and sovereignty requirements increasingly mandated by European procurement frameworks. ISO 27001 certification provides an auditable information security management system that aligns with third-party risk governance expectations under regulations like DORA and NIS2. For organizations concerned about data governance, aqua cloud maintains a clear commitment that customer data is never used for training purposes. Capabilities can be disabled if required for additional control based on your organizational policies.
Core Compliance Capabilities of aqua cloud
aqua cloud delivers specific features addressing European regulatory requirements for quality assurance and regulatory compliance:
Built-in requirements-to-test traceability – Automated bidirectional linking ensures every critical requirement connects to verification evidence. Traceability matrices are generated in real-time for instant audit responses
Immutable audit trails – Complete history tracking for requirements, tests, and execution results with tamper-evident logs. You can see who made changes, what was modified, and when actions occurred
Role-based access control – Configurable permissions enforce separation of duties, preventing testers from approving their own work. The system maintains appropriate access levels for different team roles
Evidence capture automation – Test execution automatically timestamps results, captures screenshots and logs for critical scenarios, and retains evidence according to your defined retention policies
Change impact analysis – Integrated tools identify which tests are affected by requirement changes. This enables risk-based regression test selection tied toa specific change scope
Compliance reporting – Pre-built and customizable reports provide audit packages containing requirements, tests, results, and approvals. You can export them in minutes rather than weeks
The European compliance situation isn’t getting simpler, and the new approach to regulations in QA and software is here to stay. Building defensible evidence between requirements, tests, and releases should become a regular practice for your business. aqua cloud, and AI-powered test and requirement management OS, delivers exactly what European businesses need. From complete requirements-to-test traceability and role-based access control for separation of duties to immutable audit trails and secure EU-based hosting options that align with data sovereignty frameworks. The platform’s domain-trained Copilot adds another dimension by automating test case generation from requirements. This cuts documentation time by up to 97% while ensuring your test coverage remains comprehensive and tied to specific regulatory needs. With native integrations to Jira, Azure DevOps, CI/CD pipelines, and multiple tools from your current tech stack, aqua becomes your central compliance hub without disrupting existing workflows.
Achieve 100% European regulatory framework coverage with aqua
Compliance is fundamentally an evidence problem where requirements plus tests constitute that evidence. For your European business navigating GDPR, NIS2, DORA, and sector-specific regulations, test and requirement management proves you shipped software responsibly. You need traceable processes with documented controls. Compliance-ready QA requires clear requirement governance, mandatory traceability for high-risk items, and structured test management with evidence capture. Tooling must enforce discipline. When you consistently demonstrate that requirements were testable, approved, versioned, and controlled with traceable verification evidence, you build operational resilience. The payoff extends beyond avoiding fines to include reduced release friction, customer and regulator trust, and competitive positioning.
What is test and requirement management compliance?
Test and requirement management compliance maintains documented, traceable evidence chains demonstrating how products meet regulatory requirements. The process involves structured workflows for defining requirements with approval gates. You link requirements to verification tests, capture execution evidence, and retain audit-ready documentation. For your European business, this proves to regulators exactly what was built, why you built it, and how you validated the results through regulatory compliance testing.
Which European regulations require test and requirement management?
GDPR requires demonstrable compliance through Article 5(2), making test artifacts subject to data protection controls. NIS2 mandates cybersecurity risk management, including secure development practices, while DORA establishes ICT resilience requirements for financial services. MDR/IVDR requires technical documentation and traceability for medical devices. Cloud sovereignty frameworks create procurement expectations for SaaS platforms. All share the expectation that your organization maintains documented verification evidence to comply with standards.
How does traceability improve compliance readiness?
Traceability creates bidirectional links between requirements, test cases, execution results, defects, and releases. During audits, you can instantly demonstrate which tests validated specific requirements. You show what results were obtained and how defects were addressed. Without traceability, your team faces weeks of manual evidence gathering with inconsistent documentation. Strong traceability transforms compliance from reactive scrambling to proactive evidence management that happens continuously.
What are the consequences of non-compliance in European markets?
Non-compliance consequences extend beyond financial penalties to include reputational damage affecting customer trust. You face operational disruption from enforcement actions, blocked product releases in regulated sectors, and loss of competitive advantage. For organizations across multiple European jurisdictions, non-compliance in one area can trigger cascading regulatory scrutiny. The cost of non-compliance typically far exceeds investment in proper compliance infrastructure and prevention strategies.
Enhancement of the aqua product is Martin’s main responsibility and biggest mission. His expertise covers ITIL Process Consulting, Change Management, Quality Assurance, Quality Management, and Requirements Management. Martin works in QA services for regulated industries for more than 18 years being an irreplaceable leader at…
Pavel, a Quality Assurance Consultant and Author, brings deep expertise to solving complex testing challenges. His background in software development has helped organizations transform their QA practices from reactive to proactive. Beyond consulting, Pavel develops best practice guides and case studies for aqua cloud that…
Home » Best practices » Test and Requirement Management Compliance for European Business
Do you love testing as we do?
Join our community of enthusiastic experts! Get new posts from the aqua blog directly in your inbox. QA trends, community discussion overviews, insightful tips — you’ll love it!
We're committed to your privacy. Aqua uses the information you provide to us to contact you about our relevant content, products, and services. You may unsubscribe from these communications at any time. For more information, check out our Privacy policy.